Overview
A critical severity out-of-bounds write vulnerability (CVE-2026-111497), widely known as HTTP2Shell and previously Node2Shell, has been identified in the widely used Google Brotli compression library. The vulnerability stems from an unchecked return value that allows an attacker to supply crafted Brotli-compressed data, causing the decoder to overwrite memory past the end of a buffer. This memory corruption can lead to process crashes (Denial of Service), disclosure of sensitive memory, or Remote Code Execution (RCE). Because the Brotli decoder is bundled and heavily utilized across major development environments and proxies—including Node.js, Microsoft's .NET, Python packages, Msys, Bun, and Envoy—this flaw significantly increases the risk landscape for organizations across operating systems, including Windows, Linux, and macOS.
With BigFix Inventory (BFI) and custom CIT signatures, you can:
- Identify vulnerable Brotli versions of Ubuntu, Python and Msys installations
- Detect library presence across endpoints
- Flag potentially compromised or malicious versions
Vulnerability Details:
Brotli versions:
- 1.0.3 < 1.0.10 (semver)
- 1.1.0 < 1.1.1 (semver)
- 1.2.0 < 1.2.1 (semver)
are affected by this vulnerability.
Mitigation / Safe Versions
NOTE: The following Brotli versions are not affected:
- 1.0.10
- 1.1.1
- 1.2.1
- 1.2.0-4ubuntu0.1(Ubuntu's Fix Version)
- 1.2.0-3ubuntu0.1(Ubuntu's Fix Version)
- 1.1.0-2ubuntu0.1(Ubuntu's Fix Version)
- 1.0.9-2ubuntu0.1(Ubuntu's Fix Version)
Detection and Remediation
Detection
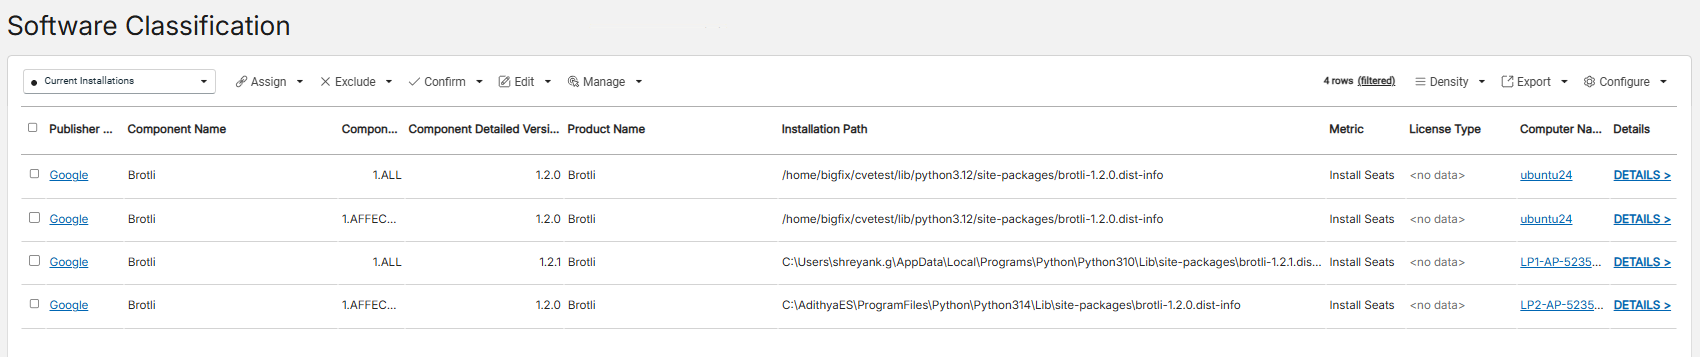
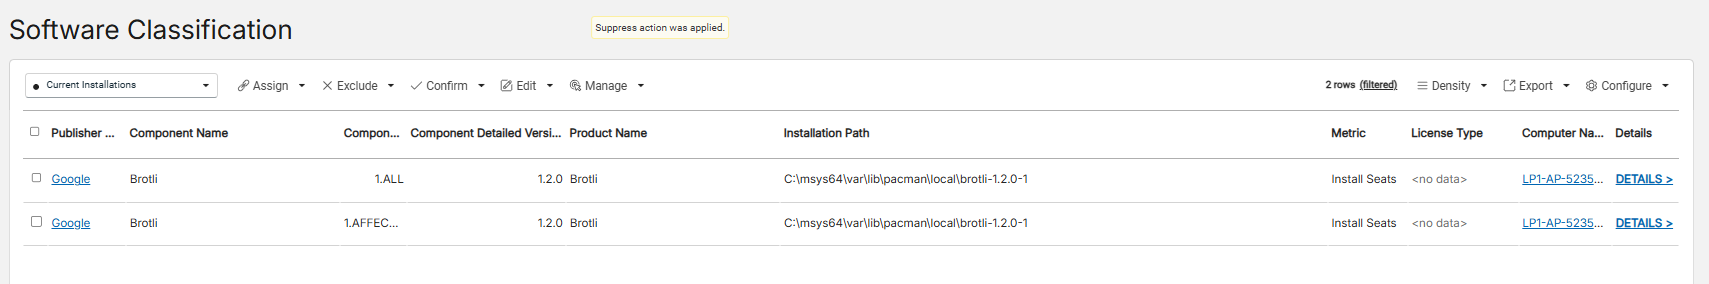
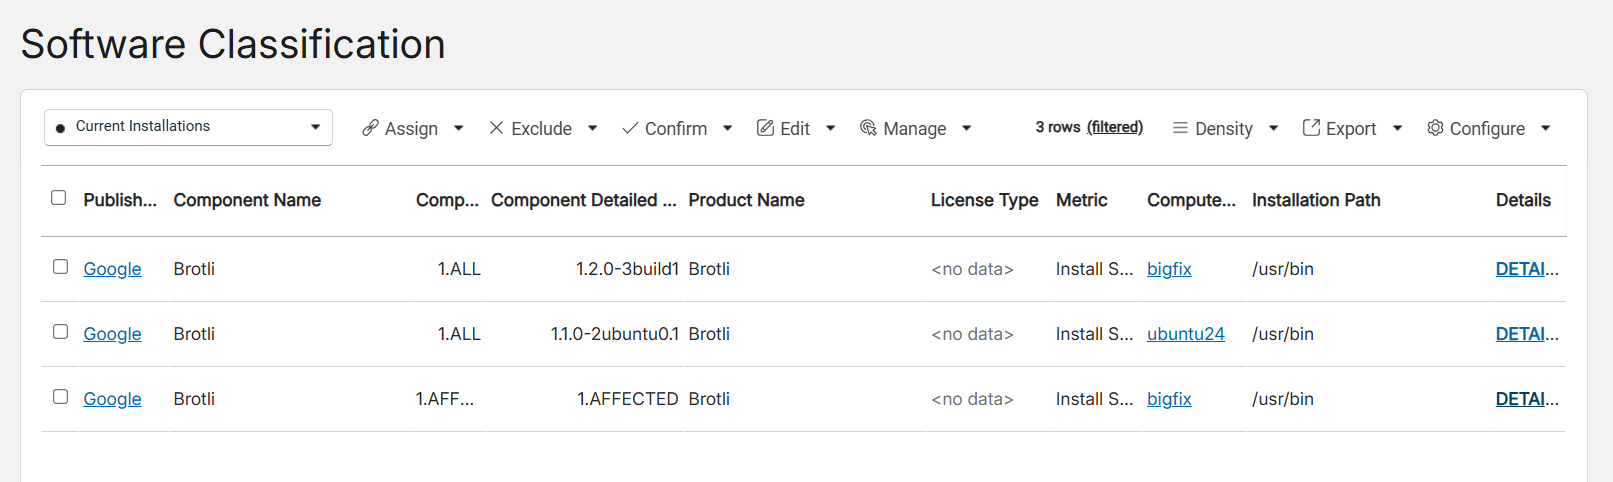
Three custom CIT signatures have been created to discover if Brotli is deployed on your environment:
- Discovery Signature
- component name: Brotli 1.ALL
- version: 1.ALL
- target: detects all versions installed in the endpoints
- Signature URL: https://bigfix.me/signature/details/1276
- Vulnerability Detection Signature
- component name: Brotli 1.AFFECTED
- version: 1.AFFECTED
- target: detects affected versions installed in the endpoints
- Signature URL: https://bigfix.me/signature/details/1275
The process for using custom signatures:
- Save the signature XML file locally.
- Login to BigFix Inventory.
- Go to Administration → Catalog → Catalog Customization (or Custom Signatures).
- Import the file with the custom signature.
- Run an import process to allow the BFI server to process the signature and initiate the signature propagation to the endpoints.
- Run a software scan on the endpoints.
- Ensure the Upload Software Scan Results fixlet is running.
- Run an import process to import the scan results.
- Verify the results on the reports.
Remediation
To mitigate CVE-2026-111497, all endpoints identified by the Brotli 1.AFFECTED signature must be updated or aligned to safe versions of the Brotli library and its consuming applications.
Update or Align to Verified Safe Versions
Ensure all standalone installations and embedded runtimes are updated or reverted to the safe releases.