Hello team,
I am trying to work on this code but not sure where to put the condition to filter only the machines with Win2019 OS version:
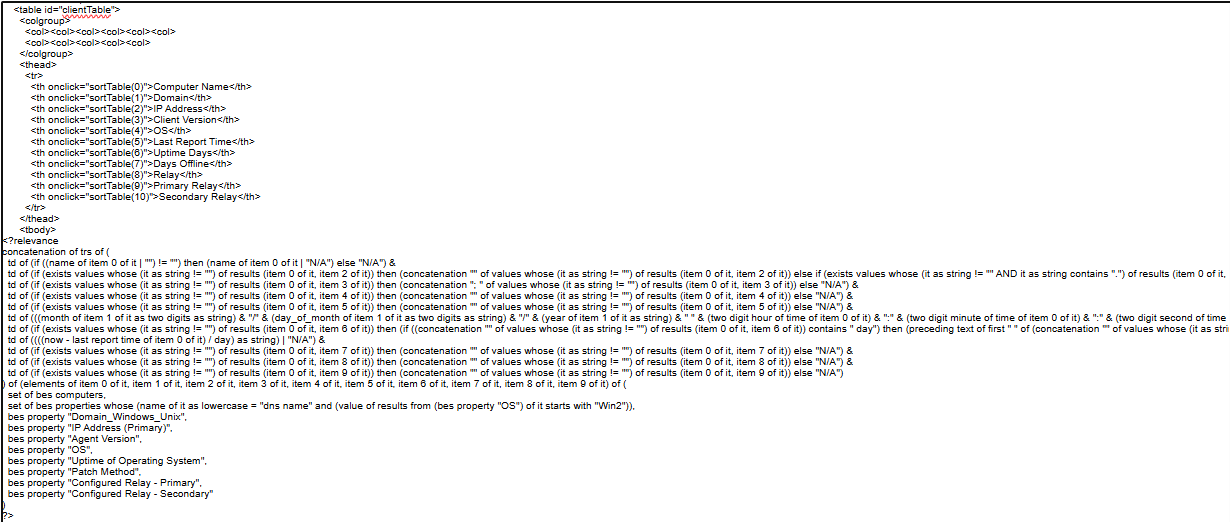
<?relevance
concatenation of trs of (
td of (if ((name of item 0 of it | "") != "") then (name of item 0 of it | "Unknown") else "Unknown") &
td of (if (exists values whose (it as string != "") of results (item 0 of it, item 2 of it)) then (concatenation "" of values whose (it as string != "") of results (item 0 of it, item 2 of it)) else if (exists values whose (it as string != "" AND it as string contains ".") of results (item 0 of it, elements of item 1 of it)) then (following text of first "." of (concatenation "" of values whose (it as string != "" AND it as string contains ".") of results (item 0 of it, elements of item 1 of it))) else if ((name of item 0 of it | "") contains ".") then (following text of first "." of (name of item 0 of it | "")) else "Unknown") &
td of (if (exists values whose (it as string != "") of results (item 0 of it, item 3 of it)) then (concatenation "; " of values whose (it as string != "") of results (item 0 of it, item 3 of it)) else "Unknown") &
td of (if (exists values whose (it as string != "") of results (item 0 of it, item 4 of it)) then (concatenation "" of values whose (it as string != "") of results (item 0 of it, item 4 of it)) else "Unknown") &
td of (if (exists values whose (it as string != "") of results (item 0 of it, item 5 of it)) then (concatenation "" of values whose (it as string != "") of results (item 0 of it, item 5 of it)) else "Unknown") &
td of (((month of item 1 of it as two digits as string) & "/" & (day_of_month of item 1 of it as two digits as string) & "/" & (year of item 1 of it as string) & " " & (two digit hour of time of item 0 of it) & ":" & (two digit minute of time of item 0 of it) & ":" & (two digit second of time of item 0 of it)) of (time (local time zone) of it, date (local time zone) of it) of (last report time of item 0 of it) | "Unknown") &
td of (if (exists values whose (it as string != "") of results (item 0 of it, item 6 of it)) then (if ((concatenation "" of values whose (it as string != "") of results (item 0 of it, item 6 of it)) contains " day") then (preceding text of first " " of (concatenation "" of values whose (it as string != "") of results (item 0 of it, item 6 of it))) else "0") else "Unknown") &
td of ((((now - last report time of item 0 of it) / day) as string) | "Unknown") &
td of (if (exists values whose (it as string != "") of results (item 0 of it, item 7 of it)) then (concatenation "" of values whose (it as string != "") of results (item 0 of it, item 7 of it)) else "Unknown") &
td of (if (exists values whose (it as string != "") of results (item 0 of it, item 8 of it)) then (concatenation "" of values whose (it as string != "") of results (item 0 of it, item 8 of it)) else "Unknown") &
td of (if (exists values whose (it as string != "") of results (item 0 of it, item 9 of it)) then (concatenation "" of values whose (it as string != "") of results (item 0 of it, item 9 of it)) else "Unknown")
) of (elements of item 0 of it, item 1 of it, item 2 of it, item 3 of it, item 4 of it, item 5 of it, item 6 of it, item 7 of it, item 8 of it, item 9 of it) of (
set of bes computers,
set of bes properties whose (name of it as lowercase = "dns name"),
bes property "Domain_Windows_Unix",
bes property "IP Address (Primary)",
bes property "Agent Version",
bes property "OS",
bes property "Uptime of Operating System",
bes property "Relay",
bes property "Configured Relay - Primary",
bes property "Configured Relay - Secondary"
)
?>
Tried adding the condition from here:
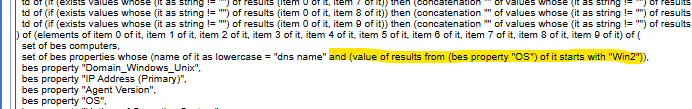
but getting the error:
The operator "results from" is not defined.
Any help will be very much appreciated. Thank you in advance
| Computer Name | Domain | IP Address | Client Version | OS | Last Report Time | Uptime Days | Days Offline | Relay | Primary Relay | Secondary Relay |
|---|