The BigFix Team is pleased to announce the availability of the BigFix MCP Server for Vulnerability Remediation, a new component that lets you plug your AI assistant of choice directly into BigFix to close the gap between a vendor publishing a patch and that patch becoming available as a Fixlet in your environment.
Zero-day response meets an open standard
The BigFix MCP Server for Vulnerability Remediation is built on the Model Context Protocol (MCP), the same open standard used by the BigFix Platform MCP Server, so any compatible AI client can connect to it through a consistent interface. The server runs as a standalone service in streamable HTTP mode, normally over HTTPS on port 9495, and every request must carry the calling user's BigFix REST API bearer token — the server never uses a shared service credential, and the token is validated against your BigFix Server before any tool runs.
What you can do with it
The new component supports the following scenario:
- CVE patch discovery: retrieve patch and optional CPE enrichment data for a given CVE identifier.
- Vendor patch file discovery: retrieve patch file metadata from the Microsoft Update Catalog, Google Chrome release/enterprise channels, and WinGet manifests, for x64, x86, and arm64.
- Fixlet generation: select an appropriate embedded BigFix template and generate reviewable BES Fixlet XML, along with a supporting result report, for the discovered CVE and patch.
This does not import content into BigFix or deploy actions to endpoints on its own — generated Fixlets must be reviewed and tested by your team before deployment, using your existing BigFix workflow.
Reliable by design, not free-form AI guessing
Every generated Fixlet is built from the same embedded templates that HCL's own patch content team has refined over more than ten years of authoring official BigFix content — the MCP server provides the AI client with retrieved patch context and steers it into that template structure, rather than letting the model draft Fixlet XML from scratch. That template-driven approach is what keeps generated content deterministic and reviewable rather than an open-ended LLM output.
Getting started
- Requirements: a supported 64-bit Windows Server environment; outbound HTTPS connectivity to your BigFix Server REST API (default port 52315) and to supported vendor services (Microsoft, Google, GitHub-hosted catalogs, port 443); an MCP client that supports remote streamable HTTP servers and custom request headers.
- Licensing: The BigFix MCP Server for Vulnerability Remediation is included in the BigFix Remediate, Starter Kit for Lifecycle, Lifecycle, Compliance, Workspace, Workspace+, Enterprise, Enterprise+ licenses free of any additional charges.
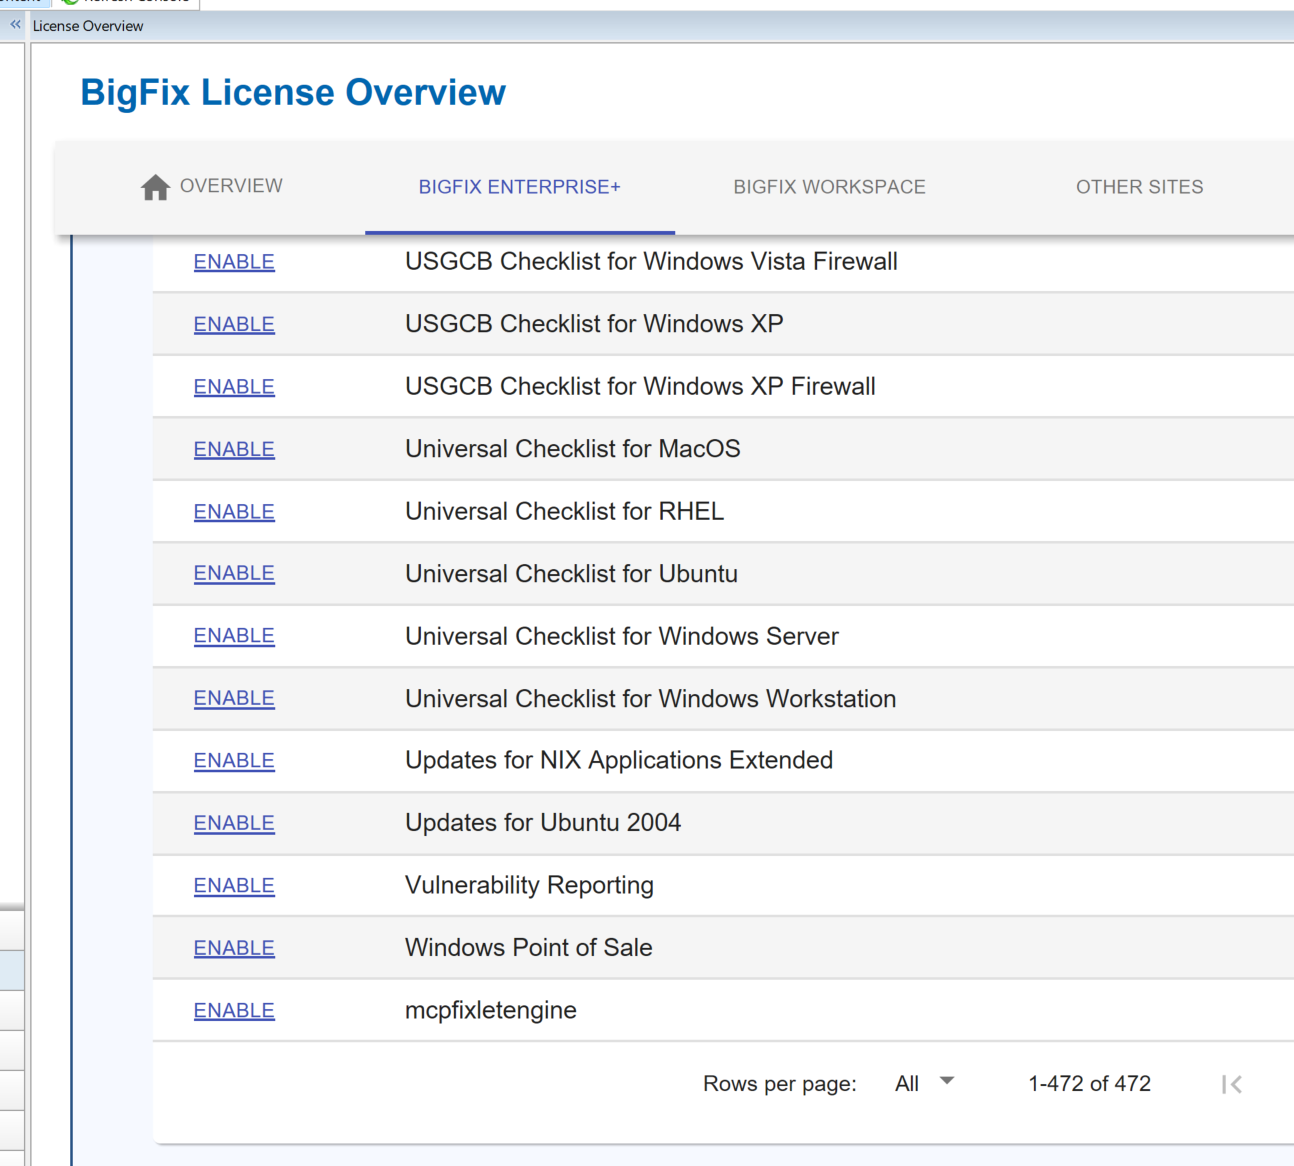
- Site Enablement: Subscribe to the ‘MCP Fixlet Engine’ site from the License Overview Dashboard. If the site is not showing in the License Overview dashboard, update your license from the dashboard by clicking ‘Check for license update’, then run the BigFix Administration Tool.
- Installation: install the package on a host that can reach your BigFix Server and configure
config.yaml
Useful links