Hi everyone,
I have a few clients who don’t show up on the BigFix console and when i look at the logs, everything looks fine except for a single that reads “Failed automatic client authentication key exchange with server message: SSL protocol not supported.”
These clients are on different networks and this is a section of the logs.
Registration Server version 10.0.15.70 , Relay version 10.0.15.70
Relay does not require authentication.
Failed automatic client authentication key exchange with server message: SSL protocol not supported.
Relay selected: a.b.c.com. at: x.y.z.d:52411 on: IPV4 (Using setting IPV4ThenIPV6)
At 16:11:22 -0400 - actionsite (http://a.b.c.com:52411/cgi-bin/bfgather.exe/actionsite)
Downloaded 'http://a.b.c.com:52411/bfmirror/bfsites/manydirlists_2/__fullsite_acde951b989369b61ae204fabbc1a78a7cb8bce2' as '__TempUpdateFilename'
Gather::SyncSiteByFile adding files - count: 388
At 16:11:23 -0400 -
Successful Synchronization with site 'actionsite' (version 180692) - 'http://a.b.c.com:52411/cgi-bin/bfgather.exe/actionsite'
ActiveDirectory: Refreshed Computer Information - Domain: (N/A)
We use port 52411 instead of 52311
Steps I have taken so far are
- Use the removal tool and reinstalled the client
- used powershell to confirm if the port is open and i got a successful connection
Please help me.
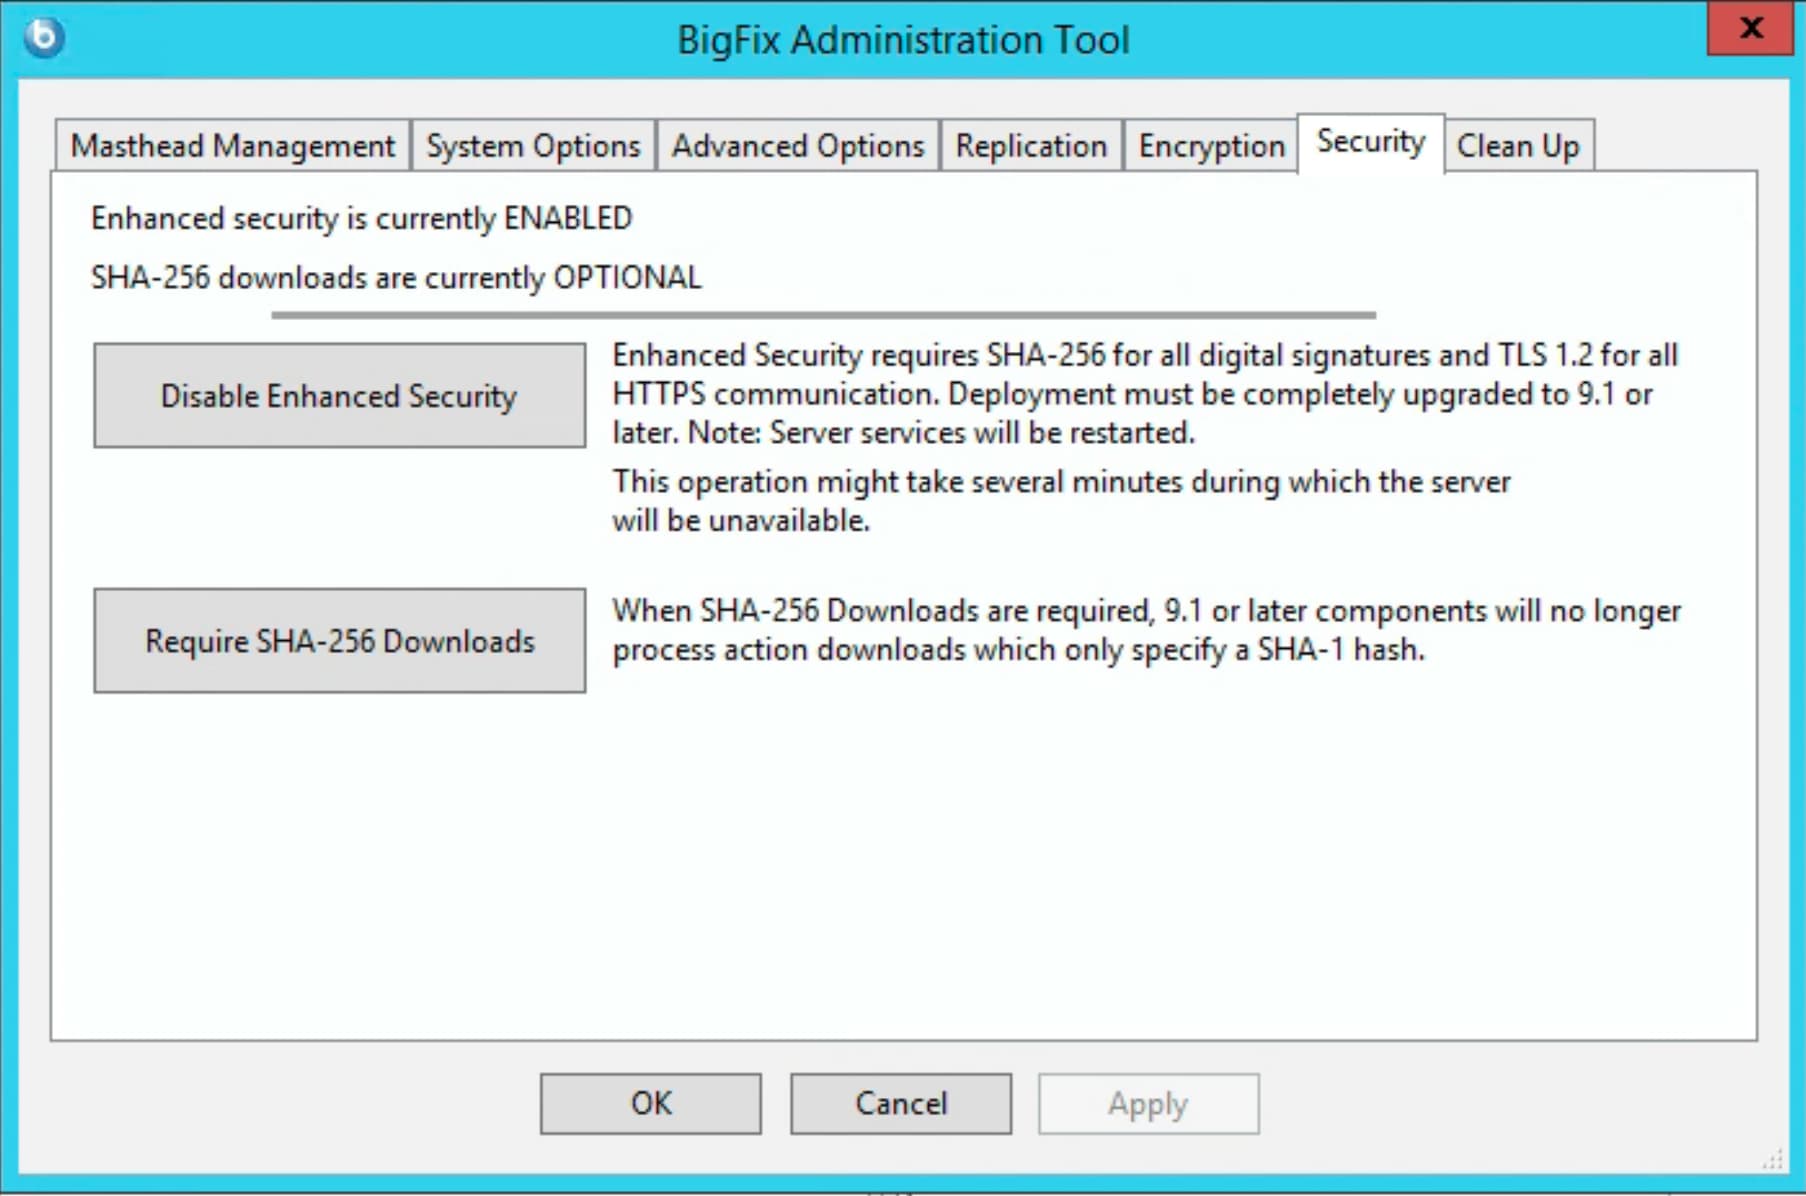
Can you check If your BigFix Security settings (via BESAdmin) or the OS on the Root Server/Relay have been locked down to strictly require TLS 1.3, the connection will be rejected. BigFix version 10 clients often initiate their registration handshakes using TLS 1.2
Additionally Open a web browser or run this curl command from the affected client to test the Layer 7 HTTPS connection:
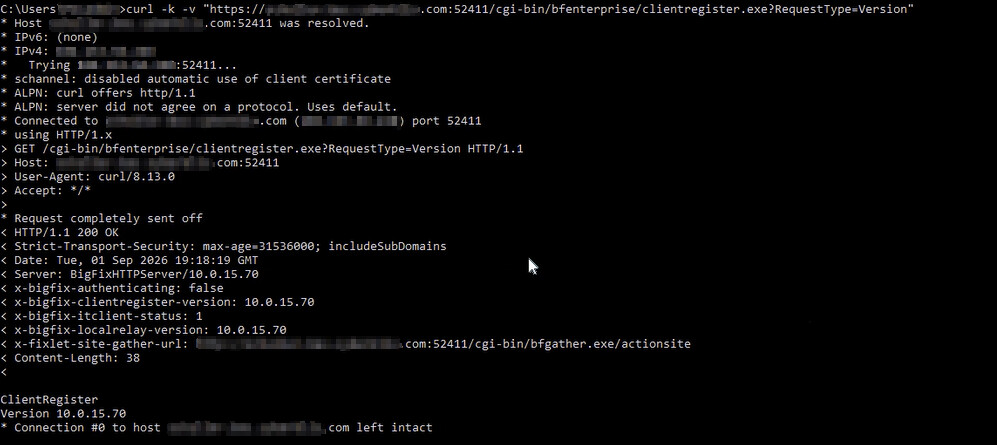
curl -k -v [https://a.b.c.com:52411/cgi-bin/bfenterprise/clientregister.exe?RequestType=Version\](https://a.b.c.com:52411/cgi-bin/bfenterprise/clientregister.exe?RequestType=Version)
If the connection times out, resets, or throws a cipher error, work with your network team. Ensure that traffic over port 52411 is explicitly allowed as HTTPS (not just TCP) and that an SSL Inspection bypass/exemption is in place for your BigFix Relays and Root Server.
2 Likes
Hi @ersaumitra10 ,
Thank you for your help. I got a hold of the admin tool and here is a screenshot of the security settings.
I am yet to run the curl command and will ley you know the outcome once it is done.
Thanks again
hi @ersaumitra10 ,
Thanks again for your help. This is a result from running the curl command
Please let me know if you need any other information. Thanks
Thank you for sharing details. I have gone through initially I thought the issue is more likely with TLS1.3 but handshake is happening.
Since the curl is ran from user account, Re-run curl, but as SYSTEM (e.g., via PsExec -s) to match BESClient's actual execution context rules out a user-profile-vs-SYSTEM cert store difference.
Check the BESClient.log on affected machine to see if any SSL/GSKit error code around the "SSL protocol not supported" line (not just the summary text)
On one affected machine, check registry: HKLM\SYSTEM\CurrentControlSet\Control\SecurityProviders\SCHANNEL\Protocols\TLS 1.2\Client confirm Enabled=1 and DisabledByDefault=0
One more step I would do is to manually perform clean re installl of bes agent on one of the affected machines to clear any stale Crypto state.
Also if zscaler or any other application is used it's worth checking with team in case any blocking is happening from their end as they apply some different policies.
1 Like
Also, I would suggest here to involve hcl support as on remote session they can look into the logs more precisely
1 Like